

Create a service key
- Go to Settings → Account Settings → Service Keys and click New Service Key.
- Enter a Key Name and choose an Account Role.
- Set an expiration date if you want. The default is no expiration. Accounts with a key lifetime limit cannot set a date past that limit.
- Click Add organizations and select them.
- For each organization, choose an Organization Role and click Add space. The default organization role is Read Only.
- For each space, choose a role. The default is Member.
- Click Create Service Key and copy the key. The key is shown only once.
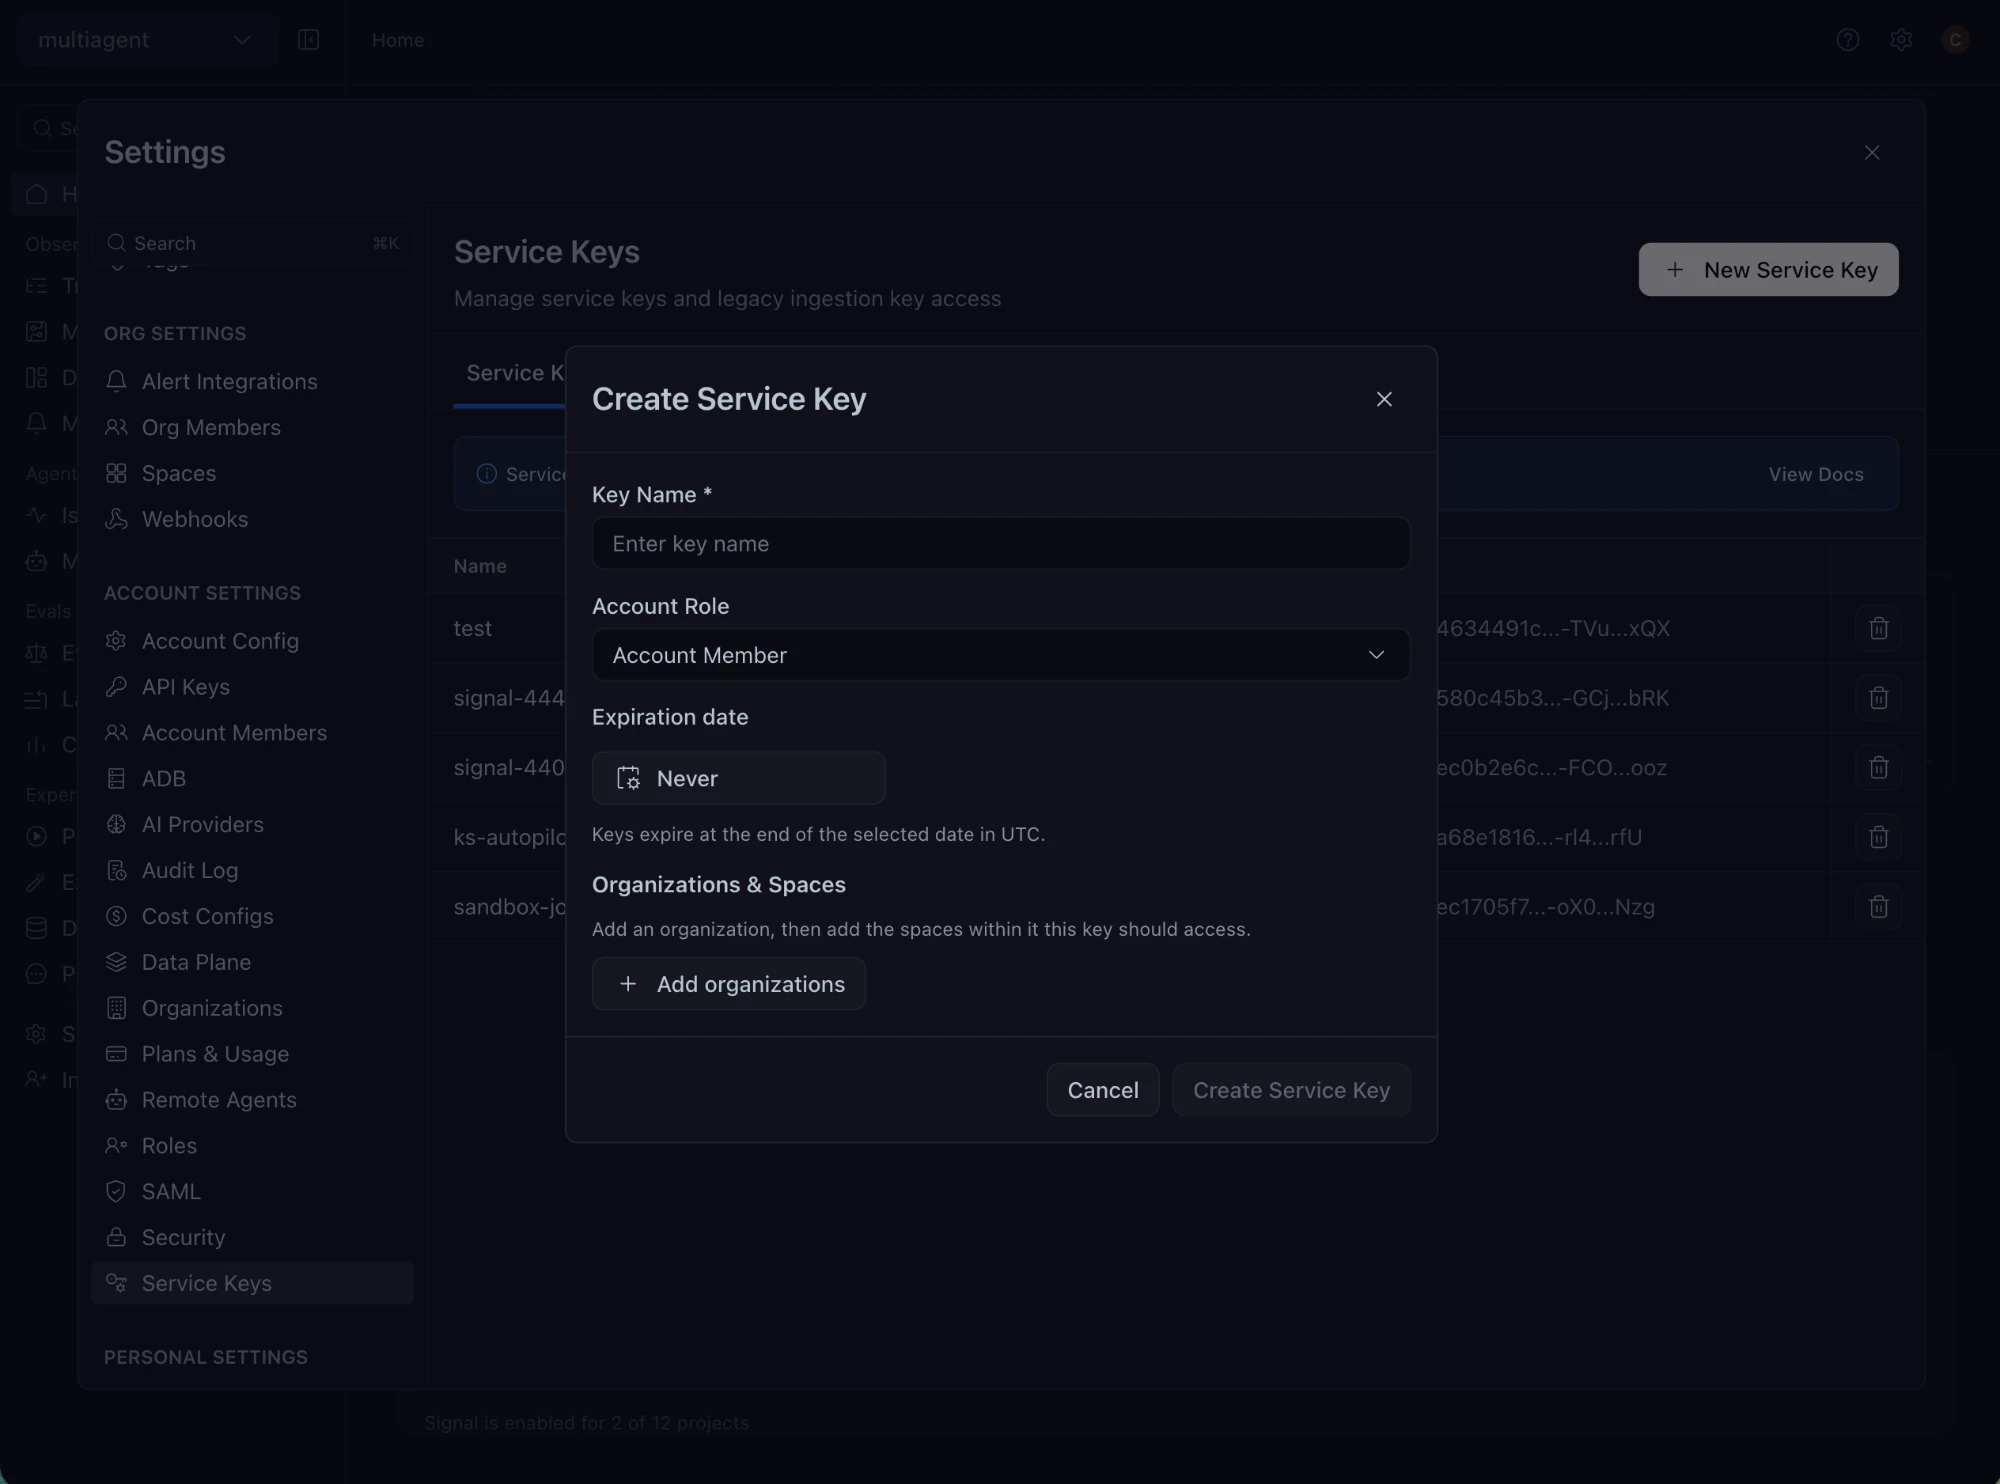
The Create Service Key dialog, with the key name, account role, expiration date, and organizations.
SERVICE_KEY_CREATE permission in every space the key covers.
Refresh a service key
Refreshing a service key issues a new key with the same name and type and revokes the old one. To avoid a gap while you update your systems, pass a grace period in the API and the old key stays valid for that period. Account admins can refresh any service key, and space admins can refresh a key if they are admins of every space it covers. Other members can refresh only keys they created, and they needSERVICE_KEY_CREATE. A refreshed key keeps the original expiration date unless you supply a new one, which cannot be later than the original.
Revoke a service key
Revoking a service key disables it in every organization and space it covers. Account admins can revoke any service key, and admins of every space a key covers can revoke it too. Other members can revoke only keys they created, and they needSERVICE_KEY_REVOKE in every space the key covers.
Nobody can create or refresh service keys while the developer access lock under Account Settings → Security is on. Existing service keys keep working.